Polylane for Security
Catch exploitable vulnerabilities before they ship
Eintragsdetails
HiCyou-Verzeichniseintrag
- Gelistedes Ziel
- producthunt.com
- Verzeichniseintrag erstellt
- 16.11.2026
- Letzte Aktualisierung des Eintrags
- 16.11.2026
Im Eintrag enthaltene Informationen
- Überblick
- 6 Kernfunktionen
- 3 Anwendungsfälle
Diese Seite beschreibt den HiCyou-Verzeichniseintrag. Sie ist keine Zertifizierung für Sicherheit, Eigentum oder Produktqualität.
Prüfen Sie die externe Website, bevor Sie sensible Informationen weitergeben oder einen Kauf tätigen.
Was ist Polylane for Security
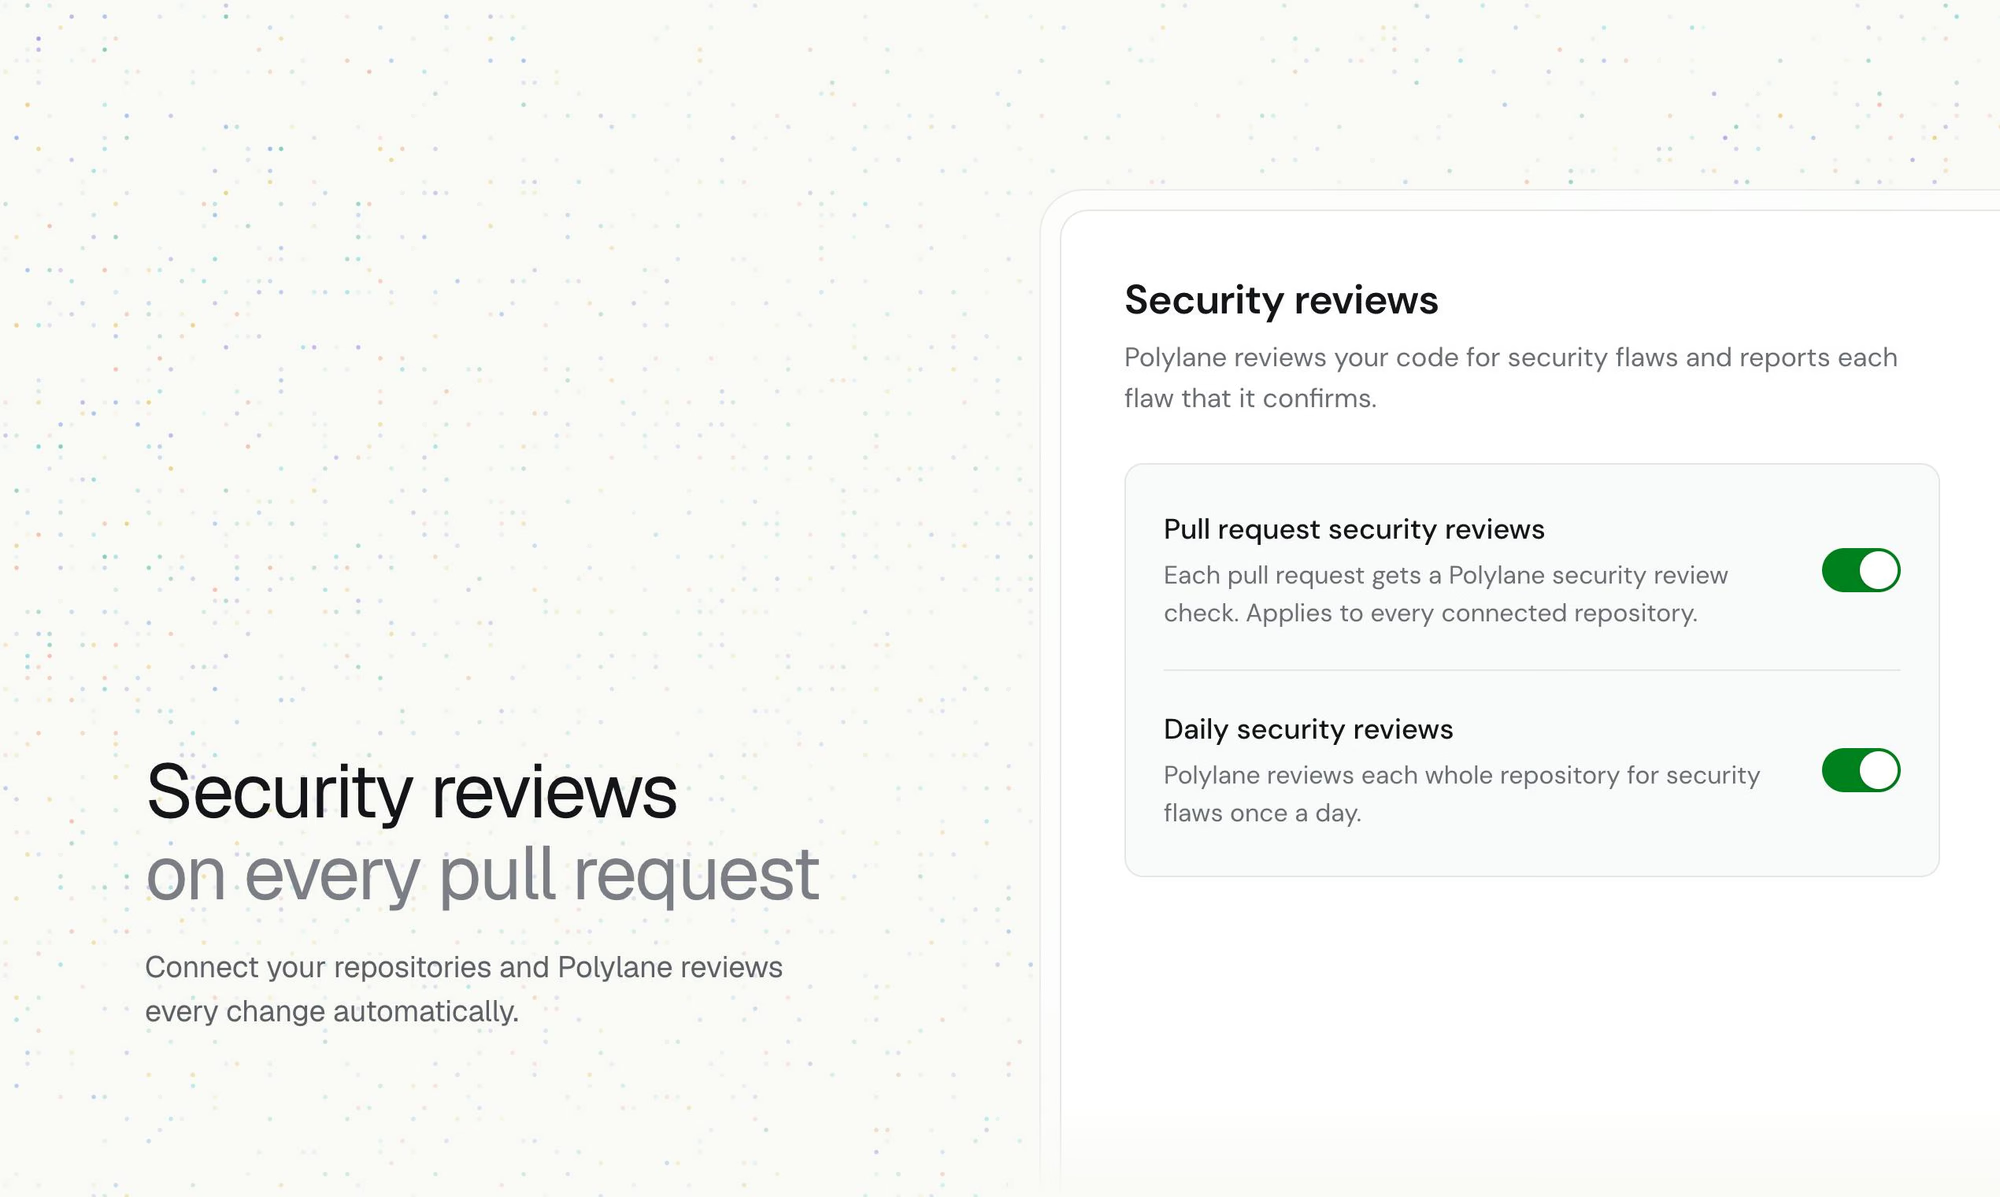
Polylane for Security is a developer security tool that reviews production-bound pull requests for exploitable vulnerabilities. Each finding traces attacker-controlled input to the vulnerable line and includes evidence and a suggested fix, while safe candidates are ruled out with a stated reason. It also runs daily dependency scans to detect known CVEs, prioritizes the most severe issues, and opens fix pull requests on active, deployed repositories.
Hauptfunktionen
Anwendungsfälle
- Screening pull requests for exploitable vulnerabilities before merging to production
- Continuously monitoring dependencies for known CVEs
- Prioritizing and remediating the most severe security issues in deployed repositories
Warum brauchen Startups dieses Tool?
Startups often lack dedicated security engineers. Polylane adds automated exploit-focused review to the pull request workflow and continuously scans dependencies, helping small teams catch exploitable vulnerabilities before they ship without slowing down delivery.