掲載情報
HiCyou の掲載記録
- 掲載先サイト
- producthunt.com
- 掲載記録の作成日
- 2026/11/16
- 記録の最終更新
- 2026/11/16
掲載されている情報
- 概要
- 主な機能 6 件
- ユースケース 3 件
このページは HiCyou の掲載記録を示すものであり、セキュリティ、所有権、または製品品質を認証するものではありません。
機密情報を共有したり購入したりする前に、外部サイトを確認してください。
Polylane for Securityとは
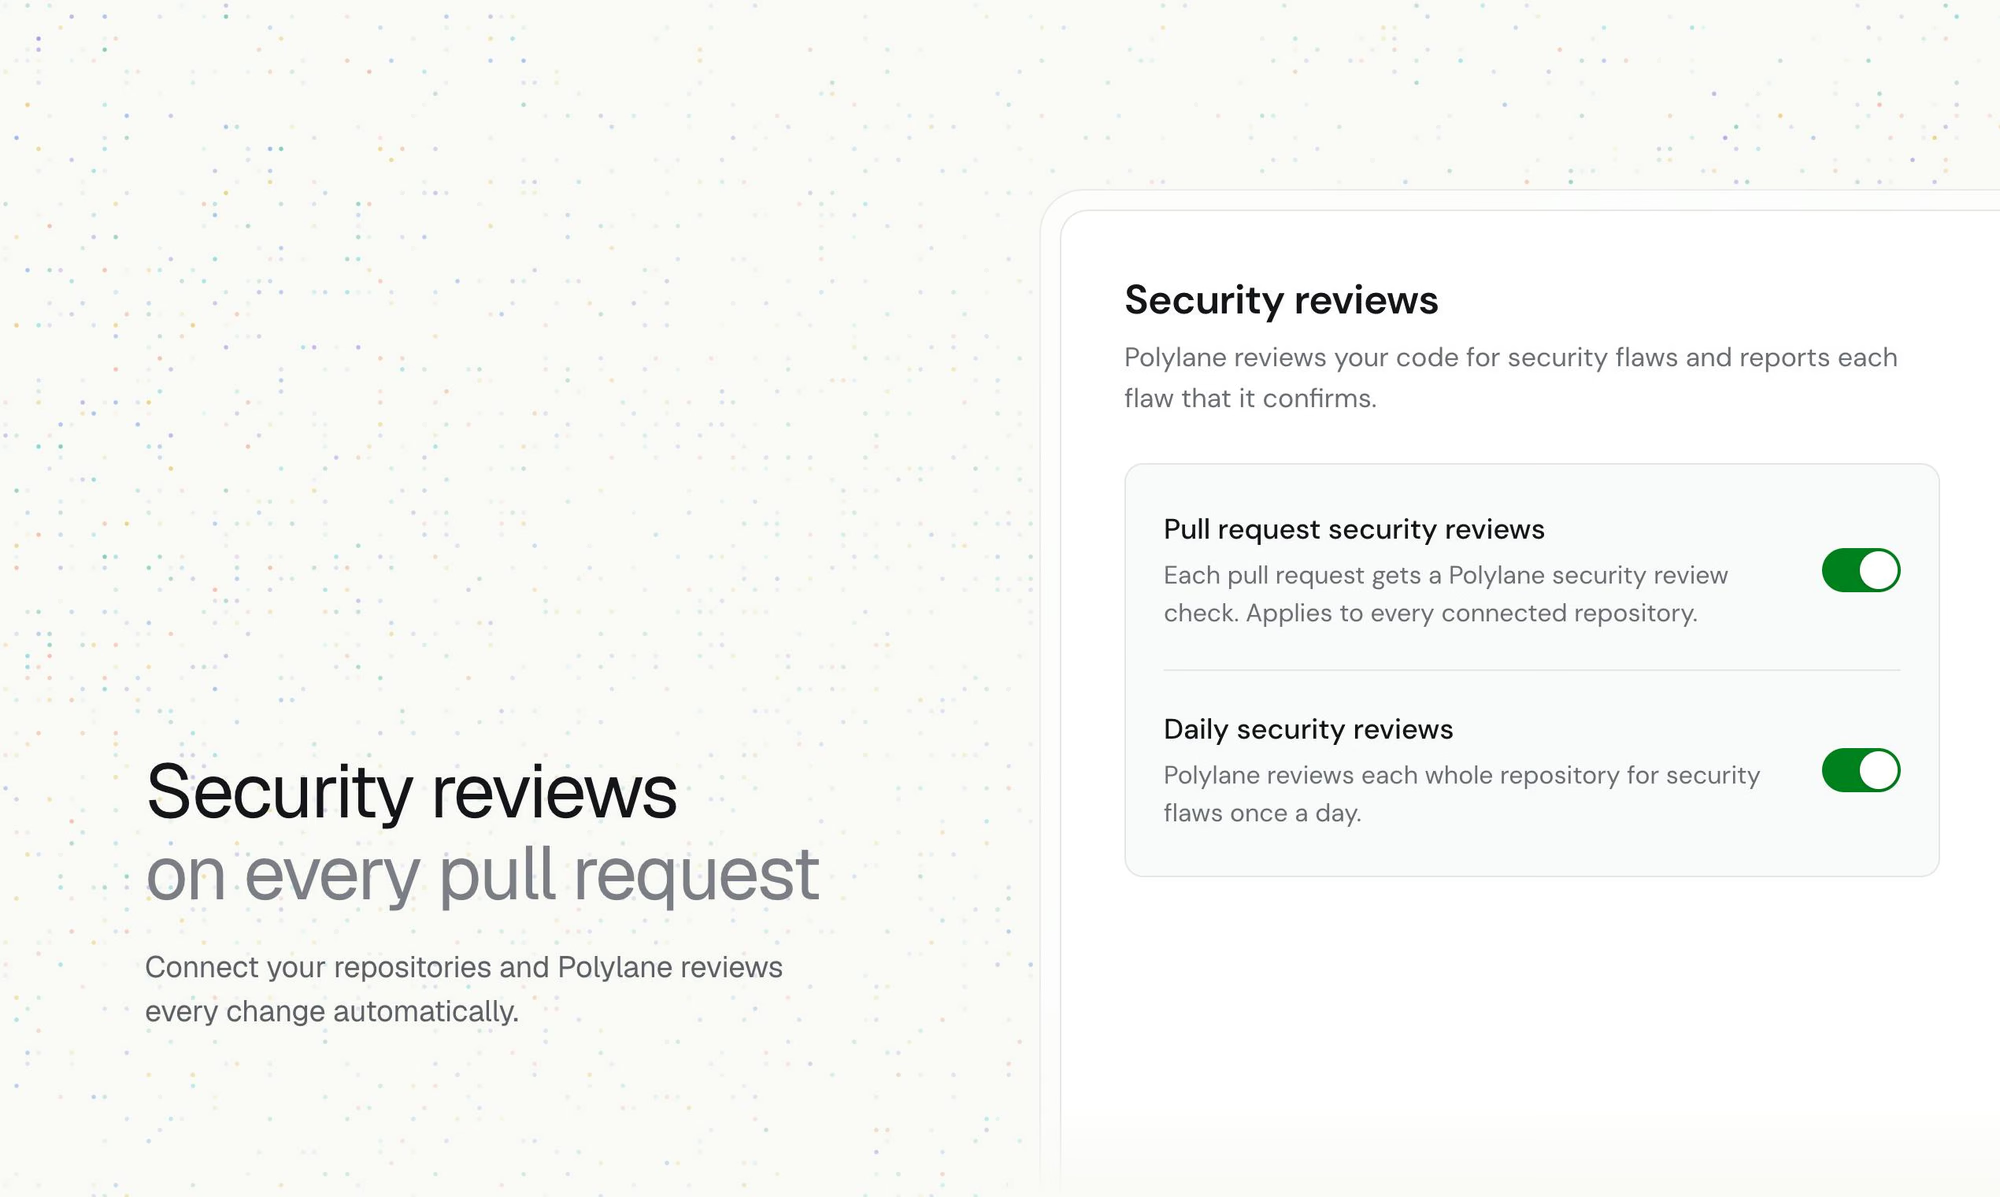
Polylane for Security is a developer security tool that reviews production-bound pull requests for exploitable vulnerabilities. Each finding traces attacker-controlled input to the vulnerable line and includes evidence and a suggested fix, while safe candidates are ruled out with a stated reason. It also runs daily dependency scans to detect known CVEs, prioritizes the most severe issues, and opens fix pull requests on active, deployed repositories.
主な機能
ユースケース
- Screening pull requests for exploitable vulnerabilities before merging to production
- Continuously monitoring dependencies for known CVEs
- Prioritizing and remediating the most severe security issues in deployed repositories
スタートアップにこのツールが必要な理由
Startups often lack dedicated security engineers. Polylane adds automated exploit-focused review to the pull request workflow and continuously scans dependencies, helping small teams catch exploitable vulnerabilities before they ship without slowing down delivery.